기능별 C2 서버를 운용하는 Kimsuky 그룹의 새로운 LNK 악성코드 등장
2026-09-09 • ESTSecurity • New Kimsuky LNK Malware Uses Function-Specific C2 Servers •
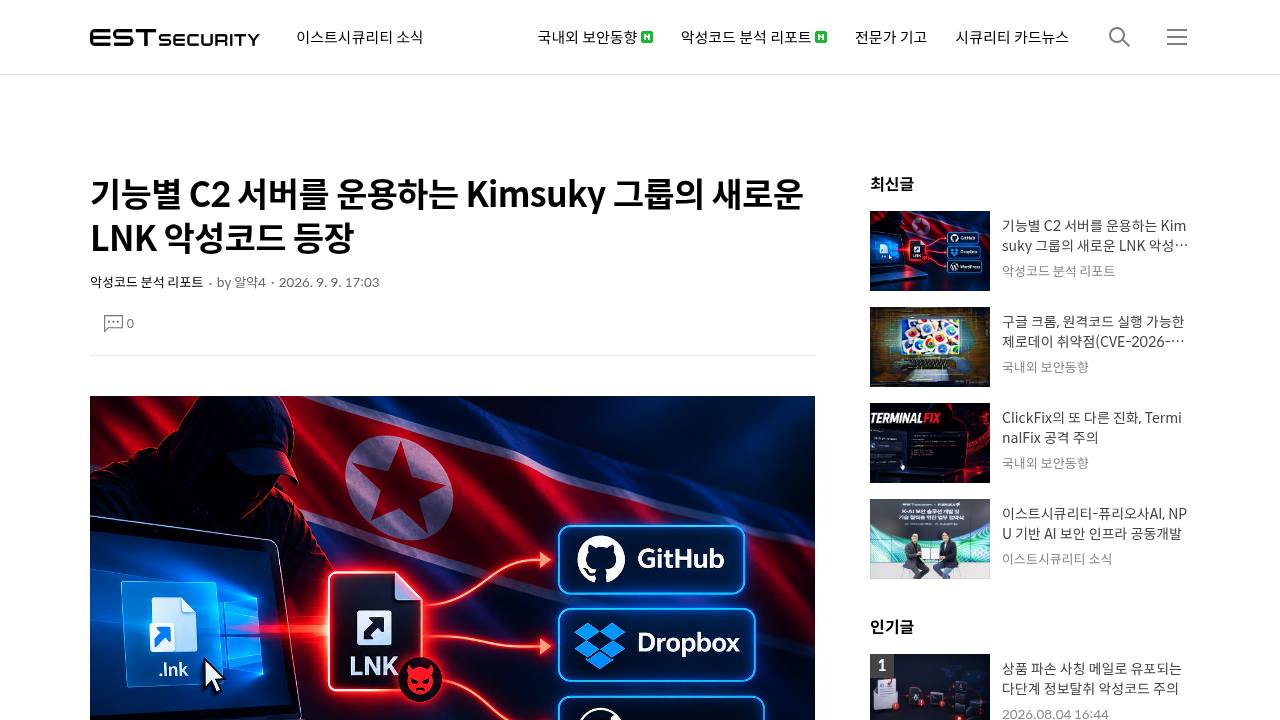
ESTsecurity attributes a new malicious LNK operation targeting South Korean organizations to Kimsuky based on the group's established shortcut-based delivery and Korean business-document lures. The chain uses batch scripts, renamed Windows utilities, and scheduled tasks to perform reconnaissance and maintain five-minute execution intervals. GitHub distributes common and MachineGuid-specific commands, a Wasmer-hosted WordPress endpoint records infection beacons, and Dropbox receives stolen data. Selected hosts can be redirected to separate repositories that reduce reconnaissance activity or deploy reverse-tunnel access through Pinggy.
Indicators of Compromise
| Type | Value | First Seen | Last Seen |
|---|---|---|---|
| DOMAIN | free.pinggy.io | 2026-09-09 | 2026-09-09 |
| URL | https://nafwo.wasmer.app/wp-con… | 2026-09-09 | 2026-09-09 |
| URL | https://raw.githubusercontent.c… | 2026-09-09 | 2026-09-09 |
| URL | https://raw.githubusercontent.c… | 2026-09-09 | 2026-09-09 |
| URL | https://raw.githubusercontent.c… | 2026-09-09 | 2026-09-09 |
| HASH | a405090029b6b95a65a8884593dfe30d | 2026-09-09 | 2026-09-09 |
| HASH | a253fa2200e4ba4d64592d87db81b8f6 | 2026-09-09 | 2026-09-09 |
| HASH | 9f99074c387083a552dcdf5ce0982ae… | 2026-09-09 | 2026-09-09 |
| HASH | 0fc425836eb854914525302b59cb830… | 2026-09-09 | 2026-09-09 |