Operation GitPower
2026-10-30 • Joe Security •
https://www.joesecurity.org/reports/report-7d62e779a769e120ac8f0c5a8bd4e968.html
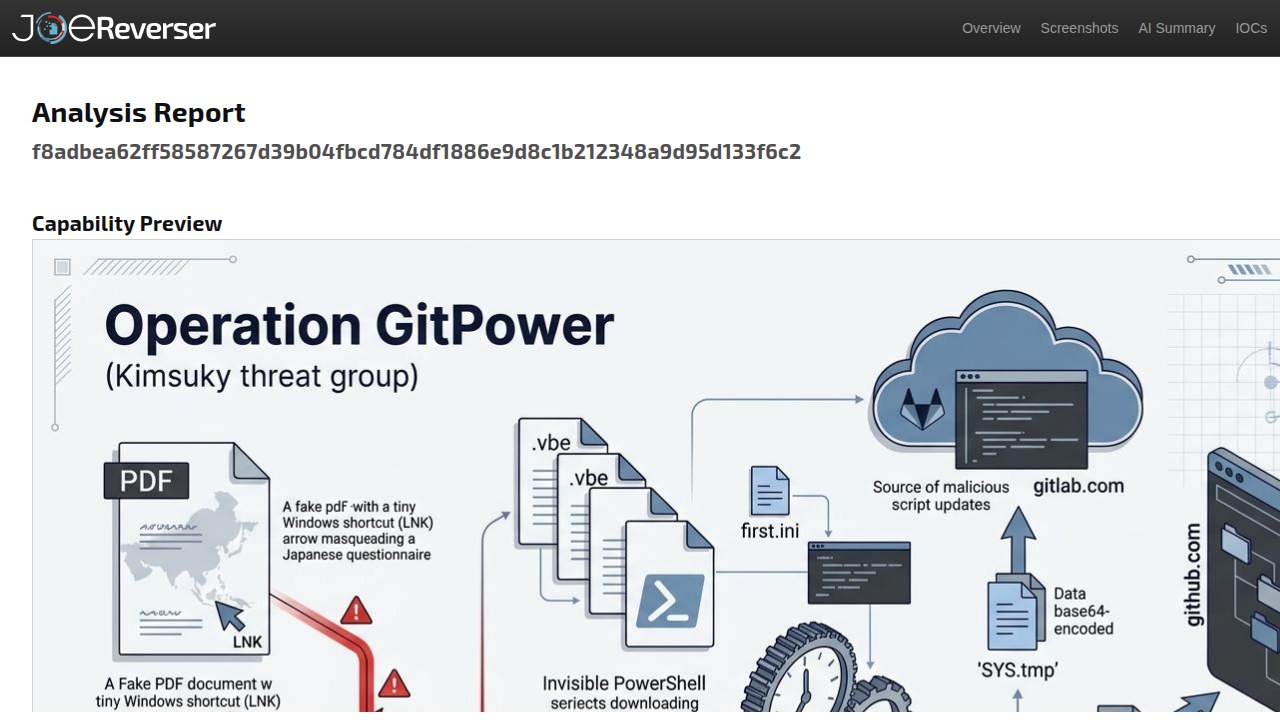
A malicious ZIP contained a PDF-disguised Windows shortcut using a Japanese foreign-policy questionnaire as its lure. The shortcut retrieved VBScript and PowerShell stages from GitLab, established 15-minute scheduled-task persistence, collected system and Downloads-directory information, and uploaded Base64-encoded results to an attacker-controlled GitHub repository. Joe Security attributed the chain to Kimsuky with high confidence because its task name, staging, obfuscation, reconnaissance, cleanup, and exfiltration design closely matched Operation GitPower. The analysis was static and did not confirm successful infection or data transfer.
Indicators of Compromise
| Type | Value | First Seen | Last Seen |
|---|---|---|---|
| URL | https://gitlab.com/rabbit779/gi… | 2026-10-30 | 2026-10-30 |
| URL | https://gitlab.com/rabbit779/gi… | 2026-10-30 | 2026-10-30 |
| URL | https://gitlab.com/rabbit779/gi… | 2026-10-30 | 2026-10-30 |
| URL | https://gitlab.com/rabbit779/gi… | 2026-10-30 | 2026-10-30 |
| HASH | 75b60302e82b599b74a0bf5fda07b9e… | 2026-10-30 | 2026-10-30 |
| HASH | b831cf5912de5460f524d0099da5506… | 2026-10-30 | 2026-10-30 |
| HASH | 385647e336913170aaea9252258a068… | 2026-10-30 | 2026-10-30 |
| HASH | 625bbefa9ad59415cd3dfd3ae16f12b… | 2026-10-30 | 2026-10-30 |
| HASH | 11551a992fe94b7cdc0df5a78074376… | 2026-10-30 | 2026-10-30 |
| HASH | cd94b4fa51812fdc4945c8dbef808fc… | 2026-10-30 | 2026-10-30 |
| HASH | 0bda23628a5955e0a089d5459631224… | 2026-10-30 | 2026-10-30 |
| HASH | f8adbea62ff58587267d39b04fbcd78… | 2026-10-30 | 2026-10-30 |
| HASH | 7d62e779a769e120ac8f0c5a8bd4e968 | 2026-10-30 | 2026-10-30 |
| URL | https://github.com/mongdolma/ka… | 2026-09-08 | 2026-10-30 |