Tracking the DPRK threat actors
for fun and profit

2026-11-18
lazarusholic

Tracking the DPRK threat actors
for fun

Why I Started

  1. 2009-07

    7.7 DDoS

    The debut stage, first contact

  2. 2013-03

    Dark Seoul

    The moment I became a real fan

    A devastating attack

  3. 2014-12

    Block Buster

    Global debut

  4. 2017-05

    WannaCry

    First ransomware

    Major global impact

  5. 2017-07

    Campaign Rifle: Andariel

    First fan letter

What I've Built

  1. 2019-07

    Prototype Unveiled

  2. 2021-09

    GitHub Pages Launch

    Managed in Google Sheets

    lazarusholic.github.io

  3. 2023-04

    Website Launch

    Database-backed, structured management

    lazarus.day

  4. 2026-07

    Major Upgrade

    LLM-assisted improvements

What Is the Goal

Collect All

Hundreds of public reports, vendor advisories, and research papers — distilled into one searchable archive of DPRK-linked actors, incidents, and indicators.
Identify All

Surface the actors behind each operation, the incidents they've shaped, and the indicators they leave behind. Every report is a starting point for attribution.

Connect All

No actor operates alone. Trace the threads that link reports to actors, actors to incidents, and incidents to the IoCs they leave behind — until the full picture emerges.

What I've Collected

  • Focused on technical reports among publicly available reports

What I Identified

  • Each report carries many kinds of clues that can link it to others
Contents Operation/Campaign TTP Vulnerability/CVE Malware/Tool CTI Report IoC Victim/Target Threat Actor

How I Connected

  • Tags are the glue between reports, incidents, and actors
Report Tag Incident IoC Actor Tagged with Tagged with Contains Attributed to Same name Same name Related Related Associated Report, Incident, and Actorare connected throughshared tags

How It Runs

  • Running Hermes Agent on GPT-6.1
Planning
Collection
Processing
Analysis
Dissemination
Feedback

Monitor RSS feeds, mailing lists, and other public sources

Summarize reports, extract and enrich IoCs, suggest tags

Identify relationships and draft reports

Publish reports and share findings
What It Shows: Reports Don't Stand Alone

What It Shows: One Incident, Many Reports

Binance

#Binance • 2026-10 • 🇦🇪 United Arab Emirates • TraderTraitor

#Cryptocurrency #FinancialGain

  • 38

    Related Reports

  • 1

    Affected Countries

  • 1

    Months Since

What It Shows: From 253 Names to 8 Clusters

What It Shows: What Naming Chaos Costs

  • Coverage Curve: share of reports retrievable with k code names

What It Shows: The Shift to Financial Gain

  • Observed shift toward cryptocurrency theft and financial gain since 2015

Tracking the DPRK threat actors
for profit

What I've Earned

Expenses

  • AI: ChatGPT $20/mo, Claude $20/mo
  • Server: Oracle Cloud Free Tier ❤️, Cloudflare Domain $10/yr
  • Hermes & Dev Server: Raspberry Pi 4 (used) $50

Income

  • AdSense: $1/mo on average
  • Buy Me a Coffee: $30/yr on average

Closing

One More Thing

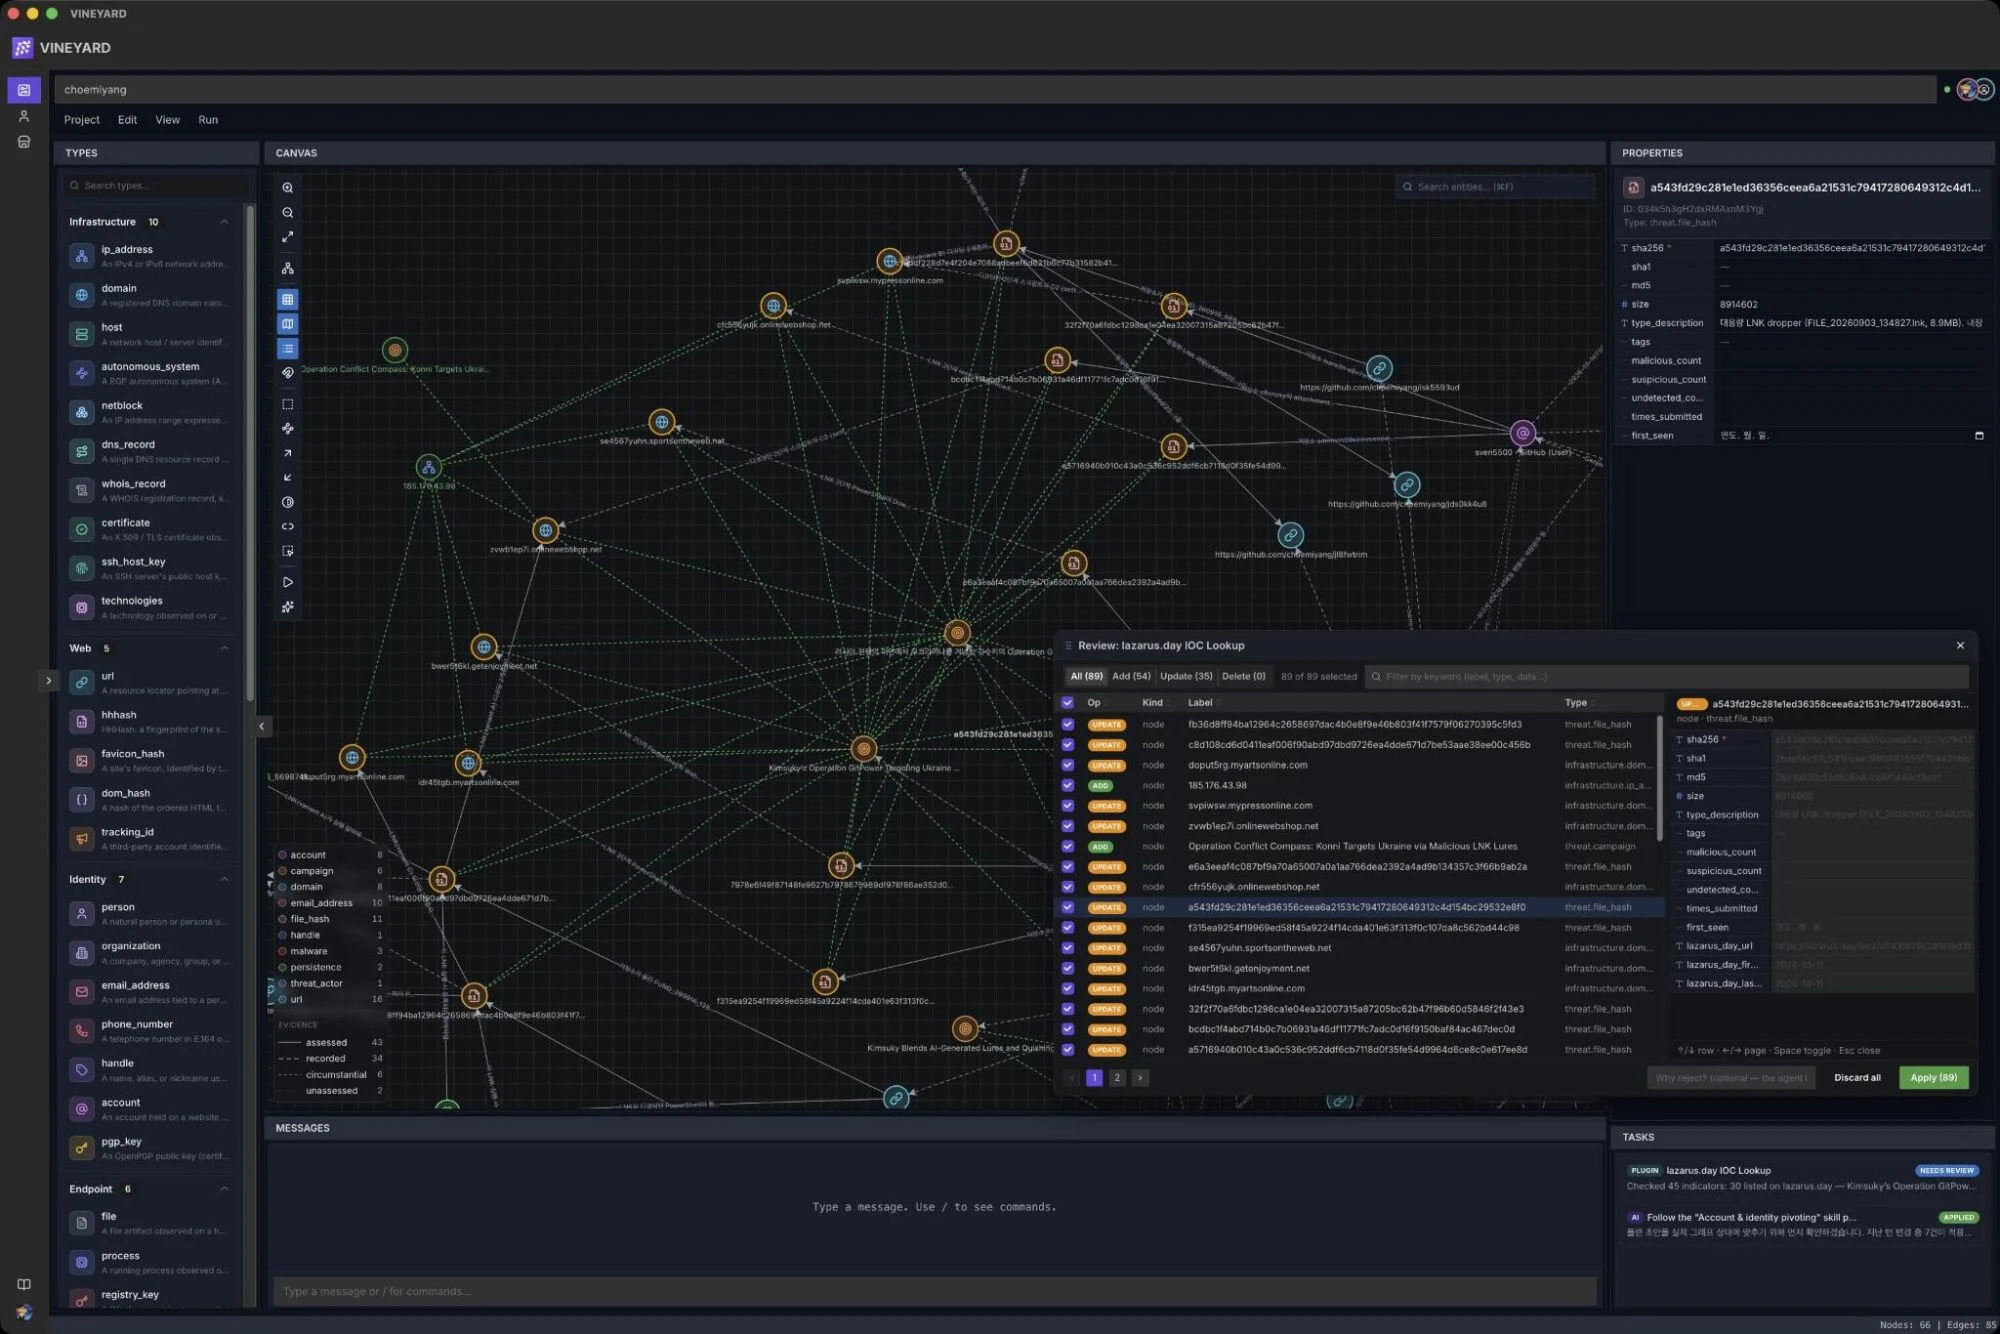
  • Vineyard: a Maltego-like tool for visualizing CTI
  • AI agents assist the investigation and reveal hidden relationships in fragmented threat intelligence
  • The Vineyard plugin can pull in lazarus.day data
  • https://vineyard.run
Vineyard workspace